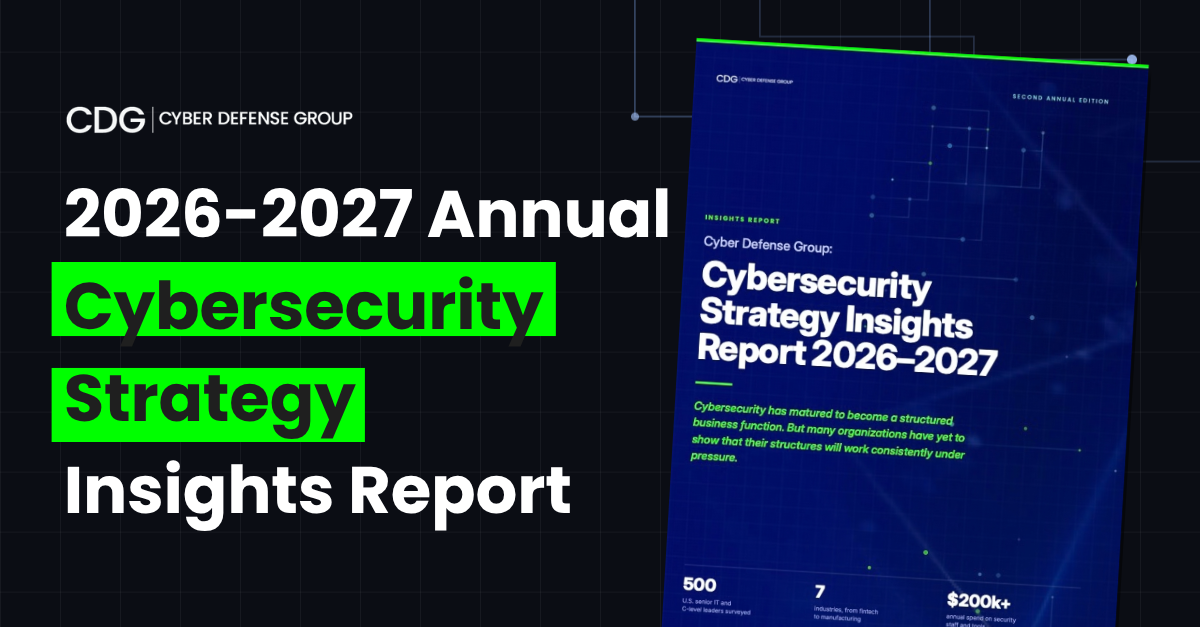
94% of IT Leaders Say They Could Contain an Incident Within 24 Hours. Only 37% Are Very Confident They Could Preserve the Evidence.
The statistics uncovered:
- 9 in 10 organizations are increasing security budgets next year. But where is the money going, and what priorities have changed since last year?
- 95% of organizations have defined an approach to external cyber risk, but only 44% have documented and communicated it. Where does your organization fall?
- Most organizations feel ready to contain an incident, but far fewer can manage what comes after. Could yours?
Building a security program is only half the job. Missed evidence makes it harder to establish cause, scope, and regulatory exposure. Inconsistent communication slows legal, commercial, and recovery decisions right when speed matters most. This report shows where organizations are strong, where they’re exposed, and what to pressure-test before a real incident does it for you.
“Putting structures and strategies in place is only half the picture. Companies need to pressure-test their systems, understand their vulnerabilities, and address any gaps before a real-world incident occurs.” – Lou Rabon, Founder and CEO, Cyber Defense Group